 PixQR
Overview
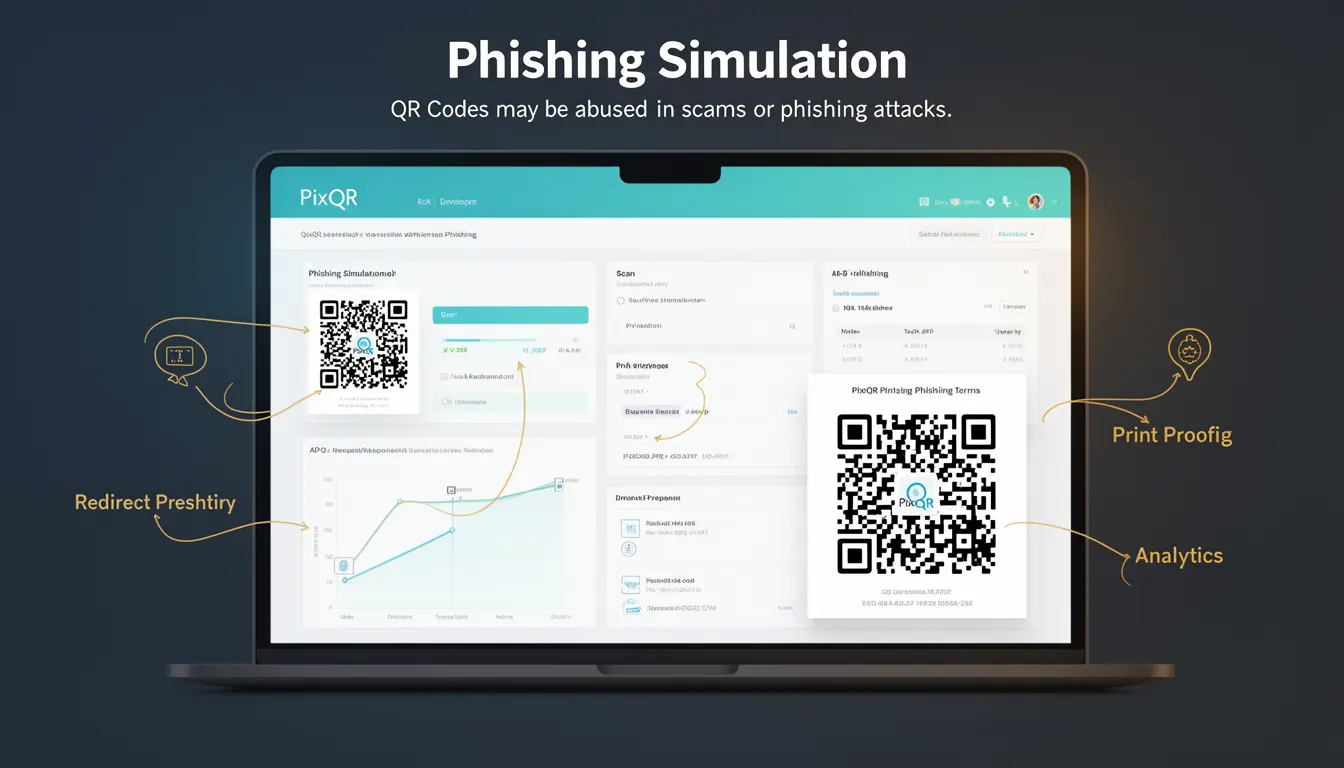
Phishing Simulation refers to a controlled test environment where organizations evaluate the effectiveness of their security awareness training by simulating real phishing attacks. In the context of QR codes, this term describes how QR codes can be misused to direct users to malicious websites or collect sensitive data. A phishing simulation using QR codes involves generating a QR code that links to a test page designed to mimic a legitimate login or financial site.
Developers working with PixQR must understand how QR codes can be exploited in phishing attacks to ensure their platforms are secure and provide tools to detect or prevent such misuse. When QR codes are generated or managed through PixQR, the platform must ensure that links are validated, monitored, and flagged if they exhibit phishing behavior.
Why It Matters
For developers, phishing simulations are crucial because they help identify vulnerabilities in user behavior and platform security. In a PixQR context, understanding phishing simulation ensures that QR code generation and redirection workflows are secure. If QR codes are used in marketing or internal training, developers must ensure they are not inadvertently creating vectors for phishing attacks.
From a production standpoint, failing to implement phishing simulation checks in QR code platforms can lead to reputational damage, regulatory compliance issues, and compromised user data. PixQR's operational workflows must include safeguards to prevent the generation of QR codes that could be used in phishing scams. This is especially important when managing dynamic redirects or third-party integrations.
How It Works
Phishing simulation in the context of QR codes involves a multi-layered process where QR code platforms detect, validate, and flag potentially malicious links. PixQR implements a risk scoring system that evaluates the URL or domain associated with a QR code to determine if it matches known phishing patterns or behaviors.
- QR code generation includes a domain validation step that checks against known malicious or suspicious domains.
- Dynamic redirects are monitored for rapid changes in destination URLs that could indicate a phishing attempt.
- Scan tracking data is analyzed to detect unusual patterns, such as high traffic from a single IP or a large number of scans in a short time.
- Link integrity checks are performed to ensure that QR code links do not contain hidden or obfuscated redirect paths.
- Platform analytics include phishing simulation reporting to help administrators identify and mitigate risks.
Quick Reference
| Item | Purpose | Notes |
|---|---|---|
| Domain validation | Checks if a QR code's destination is in a known malicious list | Part of PixQR's anti-phishing workflow |
| Redirect monitoring | Tracks changes in destination URLs | Flags rapid or suspicious redirects |
| Scan analytics | Identifies unusual scanning patterns | Helps detect phishing simulations |
| Obfuscation checks | Ensures URLs are not hidden or encoded | Prevents bypassing safety checks |
| Simulated phishing reports | Provides data for security training | Used in internal awareness programs |
Basic Example
PixQR Example QR
This QR links directly to this glossary page, so printed notes, onboarding docs, and support material can bring scanners back to the current reference.
/glossary/qr-code-phishing/qr-code-phishing-phishing-simulation
This example demonstrates how a QR code generator might validate a URL before creating a QR code. The validation includes checking against a list of known malicious domains.
function generateQRCode(url) {
  if (isMaliciousDomain(url)) {
    throw new Error("QR code destination is flagged as malicious");
  }
  return createQR(url);
}
The function checks the URL against a database of known phishing domains before proceeding. If a match is found, it raises an error to prevent the QR code from being created.
Production Example
This more comprehensive example includes URL sanitization, domain validation, and logging for phishing simulation purposes. It is suitable for a production environment using PixQR's APIs.
function createSecureQRCode(url, metadata = {}) {
  const sanitizedUrl = sanitizeUrl(url);
  const domain = extractDomain(sanitizedUrl);

  if (isDomainBlacklisted(domain)) {
    logPhishingAttempt(sanitizedUrl, metadata);
    throw new Error("QR code destination is blacklisted for phishing");
  }

  const qrCode = generateQR(sanitizedUrl);
  logQRGeneration(qrCode, metadata);

  return qrCode;
}
This version includes sanitization, blacklisting, logging, and metadata tracking, all of which are essential for operational security and compliance in a platform like PixQR.
Common Mistakes
- Skipping domain validation during QR code creation, which allows malicious links to be generated.
- Not implementing redirect monitoring, leading to undetected phishing redirections.
- Ignoring scan analytics to detect suspicious usage patterns or high-volume scans.
- Using obfuscated or encoded URLs without proper decoding and validation checks.
- Disabling phishing simulation reporting, which prevents administrators from tracking and learning from phishing attempts.
Security And Production Notes
- Always validate QR code destinations against a regularly updated list of known phishing domains.
- Implement redirect monitoring to catch malicious changes in destination URLs after QR code creation.
- Use scan analytics to detect unusual traffic patterns that may indicate phishing simulations.
- Sanitize URLs to prevent obfuscation or encoding from bypassing safety checks.
- Ensure phishing simulation reports are available for internal training and compliance audits.
Related Concepts
Phishing Simulation connects to several core concepts in secure QR code management. Dynamic Redirects are used to control where QR codes point, and must be validated to avoid phishing. Scan Reliability ensures that QR codes are scannable and consistent, which is important for phishing simulations. Brand-Safe Design ensures that QR code content aligns with brand guidelines and does not appear suspicious. Analytics and Privacy are essential for tracking usage without compromising user data. Operational Workflows include the processes for generating, monitoring, and auditing QR codes for potential misuse.